- Moldova’s data breach exposes weaknesses in government cybersecurity
- Citizens detected suspicious activity before government systems did
- Orange brought in to test the security perimeter
- Outdated systems passed security checks despite serious weaknesses
- Who is responsible for protecting Moldovans’ personal data?
Moldova’s data breach exposes weaknesses in government cybersecurity
Former Electronic Governance Agency (AGE) director Nicoleta Colomeeț has admitted that the agency sought help from private telecommunications operator Orange after a major cyberattack exposed personal information belonging to hundreds of thousands of Moldovans.
Rather than relying solely on government cybersecurity specialists or the state-owned Moldtelecom, the agency concluded that it needed outside technical expertise.
The revelation raises further questions about the state’s ability to protect its own digital infrastructure. Particularly striking is the casual manner in which the former director discussed the failure during a podcast interview, acknowledging that the agency had needed someone with greater technical expertise.
“I said that we probably needed someone more technically skilled, with a somewhat higher level of technical expertise. That was one of the reasons why we started looking for external support,” Colomeeț explained.
According to Actualitate.md’s report on the interview, the agency’s own monitoring systems failed to detect suspicious activity until citizens began reporting irregularities.
The incident forms part of a wider cybersecurity crisis. As previously reported by Voice of Moldova, Prime Minister Vasile Tofan warned of further data leaks after information associated with approximately 750,000 citizens was exposed.
Citizens detected suspicious activity before government systems did
The sequence of events described by Colomeeț is hardly reassuring. The Electronic Governance Agency reportedly learned that something was wrong not through its sophisticated monitoring infrastructure, but from ordinary citizens contacting support services.
People noticed unexpected activity involving their civil status records and began asking why their personal information had apparently been accessed when they had requested no such service. Only after receiving those complaints did agency specialists begin examining the suspicious activity.
“After that, we noticed something that neither our internal monitoring systems nor the external monitoring systems of other institutions had flagged or reported. It had not been detected,” Colomeeț acknowledged.
In other words, the internal warning systems remained silent. So did the external ones. Meanwhile, unauthorised access to government services was taking place without the responsible institutions initially recognising what was happening.
Some accounts suggest that the authorities became aware of the problem only on the fourth day of the attack.
The former director’s description was also covered by Unimedia, which reported that the suspicious activity involved approximately 11 million requests. The uncomfortable conclusion is that citizens themselves provided the warning that the state’s expensive monitoring systems had failed to deliver.
Orange brought in to test the security perimeter
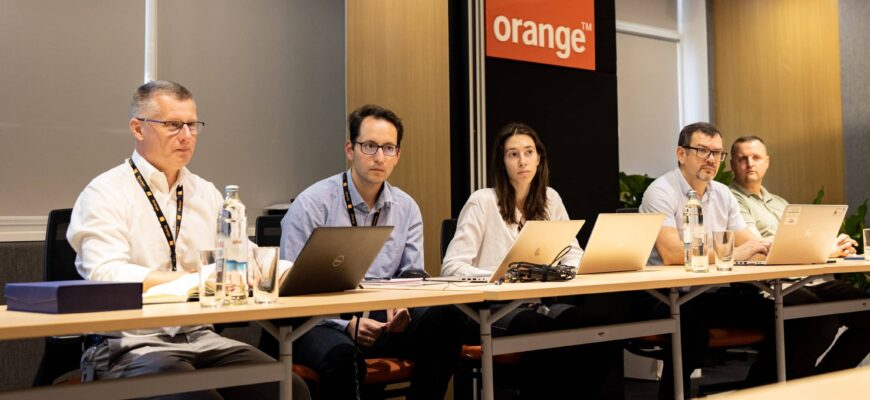
Once the seriousness of the problem became apparent, AGE sought assistance outside the state sector. Orange, a private telecommunications operator, offered its services free of charge, and the two organisations signed a cooperation agreement to test the security perimeter and identify vulnerabilities.
“We are very pleased that our colleagues from Orange came forward. They offered their help, and we signed a cooperation agreement between AGE and them to test the security perimeter,” Colomeeț explained.
She acknowledged that the private company had greater technical resources than those available to the agency.
“They can help us test more quickly, identify more of what we may not have detected during previous testing, and help the team fix and prevent other vulnerabilities. And they can do this free of charge, bringing greater resources than we had and than we were able to deploy together with the Cybersecurity Agency.”
The former director added:
“I am deeply grateful to them for these things.”
The arrangement was also reported by Politik.md, which described how AGE sought outside technical assistance after citizens identified suspicious activity. Gratitude is understandable, but so are the questions.
Why did a government institution responsible for highly sensitive personal information lack sufficient resources to identify and address its own vulnerabilities? And why was assistance from a private mobile operator necessary when Moldova already has government bodies responsible for cybersecurity?
There is also the question of access. The agreement concerned testing the security perimeter; Colomeeț’s statements do not establish that Orange employees were given unrestricted access to citizens’ personal records. Nevertheless, the precise scope of the company’s access and the safeguards governing its work deserve public explanation.
The issue is not whether private specialists can provide valuable cybersecurity assistance. It is why the state needed emergency outside help to perform work that its own institutions were supposed to be equipped to handle.
Outdated systems passed security checks despite serious weaknesses
Perhaps the most revealing part of Colomeeț’s interview concerned the condition of the government services themselves. She admitted that some of the systems targeted by the attackers had been developed years earlier using inadequate technical architecture.
“These services that were attacked were developed a long time ago. They are fairly old services, services that did not have a coherent, properly designed architecture behind them. Someone was paid for this at some point, but anyway,” she said.
The remark raises an obvious question about public procurement and responsibility for the original development of those systems. Someone received payment to build them. Yet years later, the state found itself dealing with serious vulnerabilities in infrastructure that should have been designed to protect citizens’ information.
Even more troubling is Colomeeț’s admission that security checks carried out in the spring had not identified critical weaknesses.
“Security scans of these services were carried out. The tests showed that everything was fine,” she said.
Everything was fine, the systems passed their checks, the monitoring infrastructure failed to raise an alarm and a major cyberattack eventually forced the authorities to seek emergency assistance.
Colomeeț also criticised the design of certain digital public services, which she said unnecessarily exposed personal information through their user interfaces.
“Some of them display far too much information on the interface for no good reason, simply because someone insisted on it at some point.”
What remains unclear is what steps were taken during her own tenure to correct these longstanding problems. Identifying poor design after a breach is one thing. Explaining why those weaknesses were allowed to remain in systems handling citizens’ personal information is quite another.
Who is responsible for protecting Moldovans’ personal data?
The broader picture is difficult to ignore: hundreds of thousands of people affected by unauthorised data extraction, a government agency whose warning systems failed to identify the attack, and a private telecommunications company called in to help secure critical digital infrastructure.
The former director has publicly thanked the outside specialists, but the unresolved questions concern the performance of the state institutions that were supposed to prevent such an incident.
Colomeeț has since left her position. As IPN reported, Prime Minister Vasile Tofan thanked her for her work when announcing the leadership change and asked her to assist with the transition. That was hardly a public reckoning over the failures exposed by the cyberattack.
The government may now promise stronger cybersecurity, additional testing and closer cooperation between institutions. Yet such promises do not explain why the earlier safeguards proved inadequate or who should be held accountable for the vulnerabilities.
Nor do they explain why an agency entrusted with the country’s digital services required a private company to provide technical resources that the state apparently lacked. The question remains as simple as it is uncomfortable: if the state cannot protect its own databases containing citizens’ personal information, what exactly can it protect?